AI leaves the lab. We follow what happens next.
Archive October 23, 2026 10:11 UTC
Listen to today's briefing 9:18
Signal: AI is now better at breaking code than anyone is at patching it - and the money funding it just had its worst day since June.
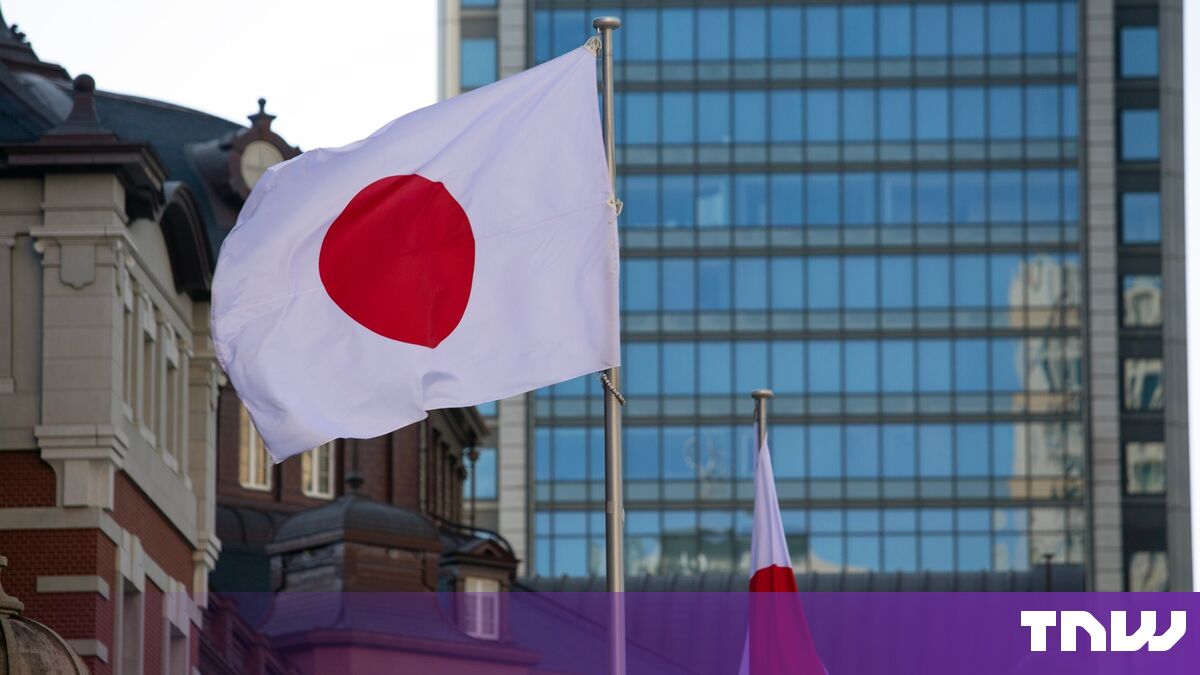
SoftBank Cuts Quake Alerts to Patch PHP2Shell
SoftBank has stopped sending earthquake, tsunami and evacuation warnings to its phones until 26 October while it patches, with Nomura, MUFG, ANA and Japan's tax agency also offline - and the first botnet attempts are failing so far.
The Hacker News: Mirai attempts fail as reliable exploitation proves harder CNN: the flaw was reported in 2004 and left unfixed for 22 years Japan's industry ministry will field an AI red team in November

OpenAI Trims Its Ask to $1.25 Trillion
OpenAI told investors Thursday it wants signatures by the end of next week on up to $30BN from Coatue and UAE funds - an opportunistic bridge before an IPO, and a month ago the ask was $1.4 trillion.
PYMNTS: OpenAI wants signatures on the round by the end of next week TechCrunch: a $1T-plus private round would set a record and raise the IPO bar
Meta's Capex Line Took the Nasdaq Down 2%
Negative free cash flow of $2.12BN and a capex floor lifted to $135BN sent Meta down nearly 7% and led the Nasdaq to its worst day since June, with the chip index off 6.72% and Seoul briefly down more than 4%.
CNBC: the Nasdaq's worst day since June as AI spending fears return Korea Times: SK hynix shelves its Solidigm listing and the KOSPI rebounds
NEWNvidia Is On the Hook for $170BN Nvidia already holds $99BN of shares in companies that buy its chips
NEWClaude Proved 123 Libraries Can't Crash A subset of the proofs is published, and Theorem will run the pipeline for others
Workbench Weekly podcast Oct 12 – Oct 18, 2026 · 17:31
Google Open-Sources Its Agent Runtime The 500ms suspend-and-resume figure is Google's own, from a 200,000-agent test
NEWAgent Wallets Had No Spending Cap Clients now cap each payment at $1 and allow only recognised dollar stablecoins
NEWLiteLLM Says Claude Code Leaked the Keys
LiteLLM says the attacker took GitHub CLI tokens that Claude Code had embedded in a response and its own internet-exposed deployment then logged, used them to switch off branch protections, and published a poisoned 1.107.0 downloaded about 49,000 times.
SecurityWeek: the package carried an infostealer and a remote-access trojan LiteLLM still cannot say how the attacker reached its exposed deployment
NEWTreasury Moves to Block AI Deals in China Biotech was added under a catch-all authority, not named in the statute's five sectors
NEWBeijing Licenses DeepSeek to Ship Abroad The approvals are reported by a state-affiliated entity, not by either company
NEWUkraine's Drones Hit Yandex Data Centers Russia's arbitration courts reportedly postponed sessions after losing database access
Ghost Note Trigger Word, Then the Cat Goes on the Stove